🔓 Event Analysis
The Binance Attack (October 30, 2026) and the Extreme Peak Signal from the EWS System
🔹 1. Overview of the Binance Attack
October 30, 2026
Early morning of October 30, 2026 (Hanoi time)
~$3 billion frozen
Including over 1.567 billion USDT and over 800 million USDC
"Binance 14" hot wallet
Attacked via a DevOps engineer's laptop
One of the most sophisticated attacks
Exploiting EIP-7702 and Privilege Escalation
The hackers did not attack directly through a source-code vulnerability but instead chose the path of manipulating internal privileges (Privilege Escalation). They infiltrated the laptop of a Binance DevOps engineer, bypassed the security layers to go straight into the service container — the server environment running the automated deposit/withdrawal service. From there, the hackers commanded Binance's automated signing system to approve malicious withdrawal transactions.
📐 Detailed Timeline of the Attack
🛡️ Why Did the Hackers Choose the Path of Internal Manipulation?
1. Avoiding Private Key Exposure
Binance confirmed that the Private Key was not exposed. The hackers instead controlled the order-signing infrastructure, making the withdrawal transactions fully "valid" to the blockchain network.
2. The Human Weak Point
The DevOps engineer holds the highest-privilege keys to the server infrastructure. The hackers implanted malware on the personal laptop via phishing or a zero-day vulnerability.
3. Abusing EIP-7702
A new Ethereum feature that allows ordinary wallets to temporarily act as smart contracts. The hackers collected 50 malicious authorization grants to force the hot wallet to delegate supreme control.
4. Lightning-Fast Attack Speed
The malicious smart contract executed the command to drain assets fully automatically at extremely high speed, before the exchange's alert system could intervene manually.
🔹 2. The PEAK Market Signal of October 28, 2026
PEAK (Local Top) - BTC SHORT
Detected by the Bitcoin PeakDip system
15:45 on October 28, 2026
~2 days before the attack occurred
$81,617.10
The peak of the rally
98% (High)
RSI hit 85.2
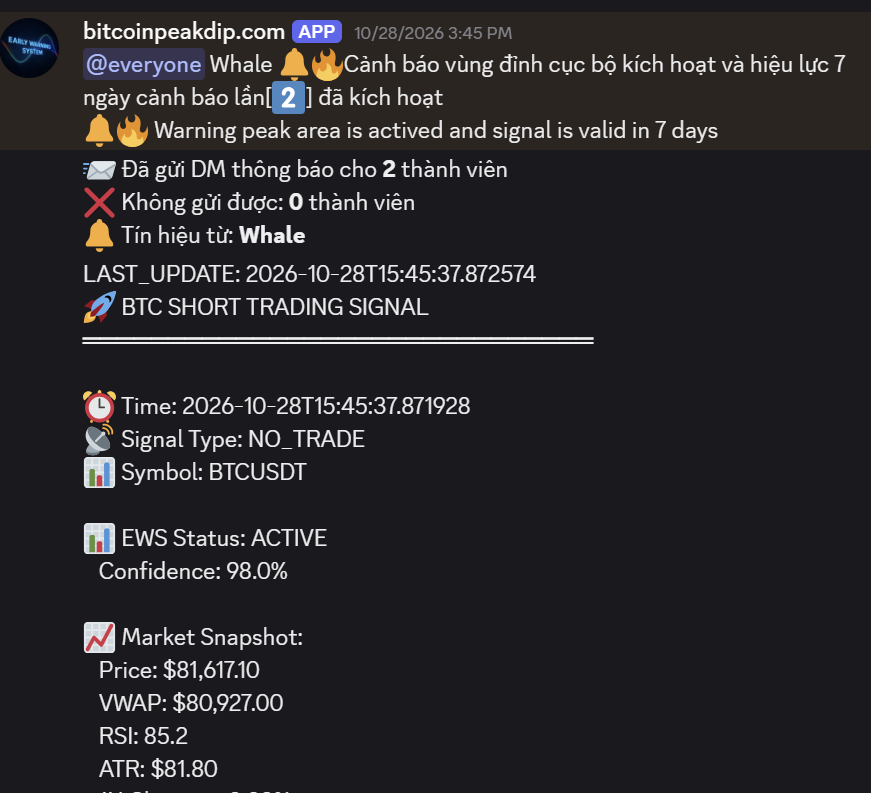
"BTC SHORT" – Extreme peak warning.
This is a warning that the market is in an overbought zone and is about to transition into a correction phase. Large funds began quietly shifting capital into a risk-distribution state.
📈 Bitcoin Price Action After the PEAK Signal
| Time | Event | BTC Price | Note |
|---|---|---|---|
| Oct 28, 15:45 | ⚠️ PEAK Signal | $81,617 | 🔔 EWS triggered – 98% confidence, RSI 85.2 |
| Night of Oct 29 | 🦢 Attack begins | ~$80,000 | Hackers infiltrate the service container |
| Morning of Oct 30 | 📉 Lockdown & panic | Breaks below $79,000 | BNB falls over 7%, long liquidation cascade |
🔹 3. The Combination Mechanism: Technical Correction + Black Swan
This is the perfect combination of two negative factors, creating a doubling effect and turning an ordinary correction into a deep and broad collapse.
🥊 The First Punch: The Market Enters a Correction Phase
- Bitcoin had risen too fast
- RSI hit 85.2 – extreme overbought zone
- Large funds began taking profits
- Selling pressure naturally increased
- The last buyers had entered
- Sellers were waiting
- The market was like a "taut string"
- Ready to snap at any moment
🦢 The Second Punch: The Black Swan
- An unexpected event with no precedent
- One of the most sophisticated attacks in history
- Caused panic and loss of trust in CEXs
- Mass withdrawals from exchanges
- The fear index dropped sharply
- Investors sold off in panic
- Binance suspended deposits/withdrawals
- The domino effect spread
⚡ When the Two Punches Combine: The Domino Effect
    🔺 BTC Price $81,617 (Peak)
         │
         │  ⚠️ PEAK WARNING issued (15:45 on Oct 28)
         │  📡 EWS triggered – BTC SHORT, 98% confidence
         │
         ├──► Whales begin selling gradually (Natural selling pressure)
         │
    🦢──┼──► THE BINANCE ATTACK OCCURS (night of Oct 29 – morning of Oct 30)
         │
         ├──► Investors sell off in panic
         ├──► Investors withdraw funds from exchanges (causing liquidity decline)
         ├──► Binance suspends deposits/withdrawals for security checks
         ├──► Users continue selling off because they cannot withdraw
         │
         ▼
    🔻 BTC Price breaks below $79,000 (Short-term bottom)
🧠 Interaction Between the Two Factors
- ✅ Investors were already in a "ready to sell" state
- ✅ Trading volume was lower (fewer buyers)
- ✅ Volatility was already high
- ✅ Technical support was weaker
- 🔥 Triggered immediate panic selling
- 🔥 The number of sellers spiked
- 🔥 Volatility exploded, liquidity was drained
- 🔥 Support levels were broken in succession
It was not the attack alone that caused the collapse, nor the natural market correction. It was the combination of the two factors that created a "Double Negative" effect, making the correction deeper and longer than usual.
🔹 4. Root Cause Analysis of the Attack
This attack is considered extremely sophisticated because the hackers did not choose to attack directly through a source-code vulnerability (smart contract exploit) but instead chose the path of manipulating internal privileges (Privilege Escalation).
👤 4.1. The Human Weak Point: The DevOps Engineer's Laptop Was Compromised
🔓 The vulnerability
DevOps engineers (Development and Operations of the ecosystem) are the people who hold the highest-privilege keys to the exchange's server infrastructure. The hackers successfully implanted malware on this engineer's personal computer (possibly through phishing scams or a zero-day vulnerability).
💥 The consequence
From the compromised laptop, the attackers bypassed the outer security layers to go straight into the service container — the server environment running Binance's automated deposit/withdrawal operational code.
🔑 4.2. The Manipulation Method: Hijacking the Order-Signing Infrastructure (No Private Key Exposure)
🛡️ How it differs from ordinary hacks
Typically, crypto hacks occur because hackers steal the private key of a wallet. However, in this case, Binance confirmed that the Private Key was not exposed.
⚠️ The "Forged Signing Through Legitimate Infrastructure" technique
Because they had control of the service operating environment, the hackers had the authority to command Binance's automated signing system to approve the withdrawal transactions they created. To the blockchain network, these withdrawal orders were fully "valid" because they were signed by Binance's own infrastructure.
⚙️ 4.3. The Exploitation Technology: Abusing Ethereum's EIP-7702 Feature
📘 What is EIP-7702?
EIP-7702 is a new technical upgrade of the Ethereum network that allows ordinary wallet addresses (EOA) to temporarily act as a smart contract (Smart Contract Wallet) to process multiple transactions at once to save costs and increase speed.
🎯 How the hackers used it
The attackers collected 50 malicious asset-withdrawal authorization grants at once using the EIP-7702 feature to force the "Binance 14" hot wallet to delegate supreme control to an unverified smart contract belonging to the hackers.
🔹 5. Lessons Learned from the Event
Always Respect Technical Signals
The market had warned of the reversal in advance. Early warning systems like PeakDip are invaluable.
Risk Management Is Supreme
No one knows when a black swan will appear. Always have a prevention plan and position management in place.
Hold Cash in Times of Uncertainty
During periods of high volatility, cash is king. Opportunities to buy in when prices fall deeply will come.
Self-Custody Your Assets
"Not your keys, not your coins" has been proven once again. A personal cold wallet is the safest solution.
Internal Infrastructure Security
Exchanges need to strengthen the security of operational personnel's personal devices, especially DevOps engineers — those who hold the highest privileges.
Coordinated Emergency Response
Binance's coordination with Tether and Circle to freeze $3 billion demonstrates the importance of cross-industry coordination in incident response.
🔹 6. Comparison with Similar Events in History
| Event | Date | Damage | Similarities | Differences |
|---|---|---|---|---|
| Mt. Gox | 2014 | ~$460 million | Major exchange hacked, loss of trust | Smaller market, no EWS signal yet |
| Bitfinex | 2016 | ~$72 million | Hot wallet attacked | Much smaller scale |
| FTX collapse | 2022 | ~$8 billion | Loss of trust in CEXs | Internal fraud, not a technical hack |
| Bybit hack | 2025 | ~$1.5 billion | CEX hacked, panic psychology | UI Spoofing, matching 98% PEAK signal |
| Binance attack | 2026 | ~$3 billion frozen | CEX attacked, panic psychology | Privilege Escalation + EIP-7702, matching 98% PEAK signal |
🔹 7. Overall Conclusion
The Binance attack of October 30, 2026 was a textbook black swan event, but its impact was doubled by the fact that the market was in a technical correction phase — warned in advance by the Bitcoin PeakDip system with 98% confidence.
7.1. Key Points
- One of the most sophisticated attacks: Binance was attacked via Privilege Escalation and EIP-7702, with ~$3 billion urgently frozen.
- Perfect timing for the collapse: The attack occurred right when the market was at its peak and preparing to correct (RSI 85.2).
- Accurate early warning: The PeakDip system issued a 98% PEAK signal at 15:45 on October 28, ~2 days before the attack.
- Double negative effect: The combination of technical correction and panic psychology pushed BTC below $79,000 and BNB down over 7%.
7.2. The Value of the Early Warning System (EWS)
- Early detection of market reversals
- High confidence (98% in this case)
- Helps investors protect their portfolios
- Combined with other factors for a comprehensive view
- Cannot predict black swans
- Only valuable if respected and acted upon
- Needs to be combined with risk management
1. Always monitor early warning signals from reputable systems.
2. Combine technical signals with news monitoring and abnormal event tracking.
3. Do not ignore reversal signals because "this time will be different."
4. Self-custody your assets to avoid risks from exchanges.
🔹 8. References & Related Articles
📄 White Paper & Official Reports
📡 Follow EWS Signals
Receive Bitcoin peak zone alerts and Altcoin collapse detection before the market reverses.